Easy Web Challenge
I am a Security guy, who develops and hacks the application.
CHALLENGE DESCRIPTION:
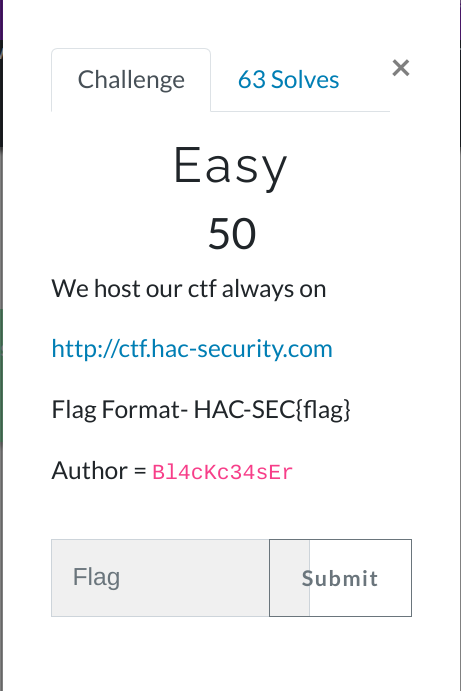
1)Locate the given url
2)Right click and select view page source
3)Scroll down
4)You can see the flag in comments
<!--HAC-SEC{TheFirst1}--!>
Search for a command to run...
I am a Security guy, who develops and hacks the application.

1)Locate the given url
2)Right click and select view page source
3)Scroll down
4)You can see the flag in comments
<!--HAC-SEC{TheFirst1}--!>
No comments yet. Be the first to comment.
CHALLENGE DESCRIPTION 1) Challenge file is same for these two challenges (i.e.,)File is same for "commenting is the key" and this 2)As per the description we need to find the ip of the pereson who entered wrong credientials 3)Looking into the file, ...
CHALLENGE DESCRIPTION 1) Download the pcap file 2)Open it with wireshark 3)Let's analyse the packets 4) If you look closely,the flag is located in packet comments. vishwaCTF{packets_are_editable}
challenge description: 1)Download the image 2) When seeing this image we have no idea But... 3)After doing some research we found that this is an "yautja cipher" 4)Using the above image we found that Iamn0talien 5)Separate it into words I_am_n0t_...
CHALLENGE DESCRIPTION: 1) Download the given file. 2)Give it execute permission chmod 700 run 3)Run the file ./run 4)Get the flag shaktictf{and_that's_how_you_run_a_linux_binary!}